

instagram-services.com
Category: Phishing
- Don't sign in or pay here. Close it. If you typed a password, change it where you normally use it.
- Already visited? Check your device. A free scan shows whether anything was installed.
- Stop the next one. Combo Cleaner's web protection blocks phishing and scam sites before they load.
Combo Cleaner is PCrisk's own anti-malware tool, owned by RCS LT. Free to scan; removing what it finds needs a licence (7-day free trial).

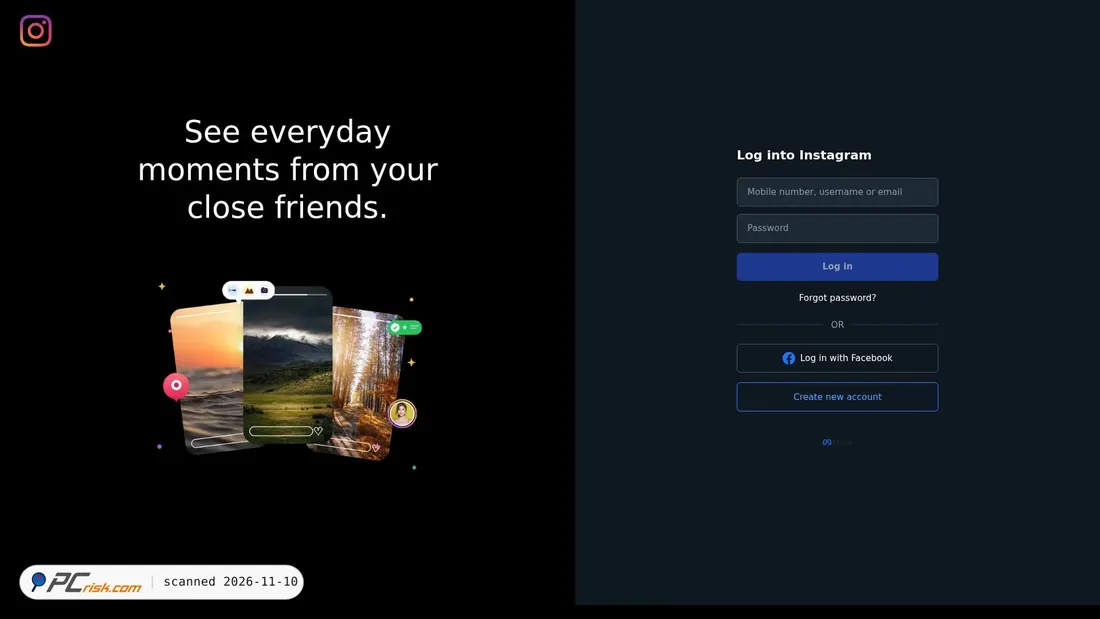
Description of instagram-services.com
The domain instagram-services.com appears to be set up to mimic Instagram rather than operate as an independent service. Based on the page content and screenshot, it presents an Instagram-style login interface with the text "Log into Instagram" and branding elements associated with that platform, while using a separate domain that is not the official instagram.com site.
The page metadata suggests a simple web application deployment, with a generic title of "Create Next App" and a default meta description. This may indicate a quickly assembled frontend hosted on a cloud platform. Based on available data, the site appears intended to collect login or other sensitive user information by presenting itself as a well-known social media service.
Safety Assessment for instagram-services.com
This website appears to pose significant risk at the time of this scan. Multiple security engines flagged the domain for phishing or malicious activity, and a major threat database listed it for social-engineering behavior. A separate page-content check also found that the site presents itself as Instagram and asks visitors to log in or provide account-related details, which is consistent with phishing behavior.
The domain name closely references the Instagram brand while using a non-official domain, and the screenshot shows a login page styled to resemble Instagram. That kind of presentation may be intended to mislead visitors into believing they are interacting with the real service. Although one malware scan reported no directly flagged files, it also produced generic malicious-object detections on site resources, which does not outweigh the broader phishing consensus.
There is also a secondary reputation concern: the domain's IP address is listed on one mail-reputation blocklist. On its own, that would be a weaker signal, but in this case it appears alongside substantial phishing-related detections and a deceptive login page. Based on these findings, this website may pose potential risks to visitors.
Technical Description
The site is hosted on Vercel infrastructure and resolves to IP address 216.150.1.1 in Walnut, United States. It uses a valid Let's Encrypt SSL certificate expiring in December 2026, which means the connection may be encrypted in transit, but encryption alone does not indicate legitimacy. The page assets and metadata suggest a Next.js-based deployment, including static chunk files and default application metadata.
DNSSEC appears to be unsigned, and the domain uses GoDaddy nameservers. No major TLS misconfiguration is evident from the provided data, but the technical setup appears consistent with a lightweight cloud-hosted web app that could be deployed quickly. The primary concern here is not the hosting stack itself, but the apparent use of that infrastructure to imitate a well-known login page.
Share your experience with this website. Was it safe? Did you encounter any issues?