

instagram-login.desireblueuniforms.com
Category: Phishing
- Don't sign in or pay here. Close it. If you typed a password, change it where you normally use it.
- Already visited? Check your device. A free scan shows whether anything was installed.
- Stop the next one. Combo Cleaner's web protection blocks phishing and scam sites before they load.
Combo Cleaner is PCrisk's own anti-malware tool, owned by RCS LT. Free to scan; removing what it finds needs a licence (7-day free trial).

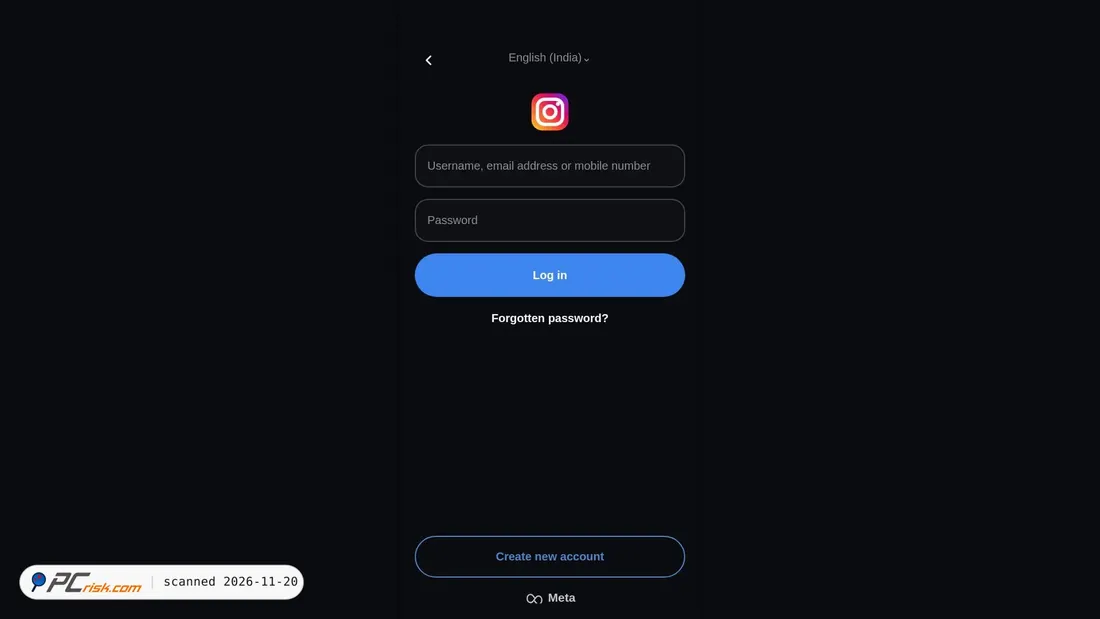
Description of instagram-login.desireblueuniforms.com
This domain appears to host a page titled "Instagram Login" that presents a login interface styled to resemble Instagram, including references to Meta and account access options. Based on the domain structure, it is not located on Instagram's official domain and instead uses a subdomain of desireblueuniforms.com, which suggests it is not an official Instagram-operated login page.
Available classification data associates the page with phishing and fraud-related categories rather than a legitimate social media service. The page content shown in the scan indicates that it asks visitors to log in or enter account details while presenting itself as Instagram, which is consistent with credential-harvesting behavior often seen on impersonation pages.
Safety Assessment for instagram-login.desireblueuniforms.com
This page appears to be a phishing page impersonating Instagram. The scan data indicates that it presents itself as a well-known company it does not belong to and asks visitors to log in or enter account details. Multiple web-classification providers categorized it as phishing or fraud-related, and 21 security engines flagged the URL for phishing or malicious activity at the time of this scan.
Threat-database results also strengthen that assessment. The URL was listed for social-engineering activity by a major browser-protection blacklist, and it was also listed by another phishing-focused threat database. In addition, the domain's IP address appears on one mail-reputation blocklist; that signal is weaker than direct phishing detections, but it adds a small amount of supporting concern.
Although the basic malware crawl did not detect flagged files during this particular check, that does not outweigh the strong phishing consensus and the page's apparent impersonation of Instagram. Based on these findings, this website may pose potential risks to visitors.
Technical Description
The site was reachable over HTTPS with a valid Let's Encrypt certificate at the time of the scan. It appears to be served by Apache from IP address 162.214.80.40, hosted on infrastructure attributed to Oracle Corporation in Phoenix, United States. The domain is several years old, registered through GoDaddy, and uses the nameservers NS1.BLUEHOST.IN and NS2.BLUEHOST.IN.
DNSSEC appears to be unsigned, which means DNS responses may not benefit from that additional integrity layer. No malicious files, external links, or iframes were identified in the limited page scan provided, but the stronger concern here is not file-based malware; it is the apparent credential-harvesting behavior and the broad phishing consensus in security detections.
Share your experience with this website. Was it safe? Did you encounter any issues?